 TyagiHub
Shield — Cybersecurity Awareness
Free cybersecurity awareness in English — for students, families, and every internet user. No jargon. Simple and clear.
The Ultimate Privacy Center Guide: Browser Security, App Permissions & Location Tracking
Your complete guide to digital privacy. Learn how to secure your browser from trackers, lock down smartphone app permissions, stop location surveillance, and build an impenetrable privacy shield around your digital life. Detailed, actionable, and India-relevant.
Dark Web & Data Breach Guide: What Happens to Your Stolen Data and How to Fight Back
When your data leaks in a breach, where does it go? This comprehensive guide explains exactly how the dark web operates, what stolen data is worth, how to check if you've been breached, and the precise step-by-step actions to secure your identity before it's too late.
Identity Theft Guide: How Criminals Steal Your Identity and How to Fight Back
Identity theft is the fastest growing crime in the digital age. This comprehensive guide explains exactly how modern identity theft works, the warning signs you're a victim, and a precise step-by-step recovery plan to reclaim your digital and financial life.
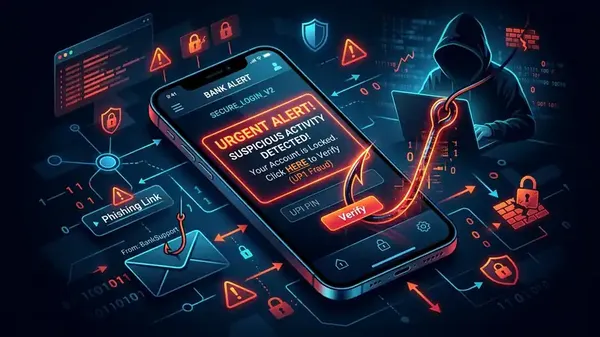
India Online Scam Guide: UPI Fraud, Phishing & Fake Customer Care | How to Protect Yourself
India is the fastest growing target for online scams. This master guide covers every major scam type — UPI fraud, phishing, fake customer care, investment scams, job scams, and more — with the exact psychology criminals use and how to stay safe.
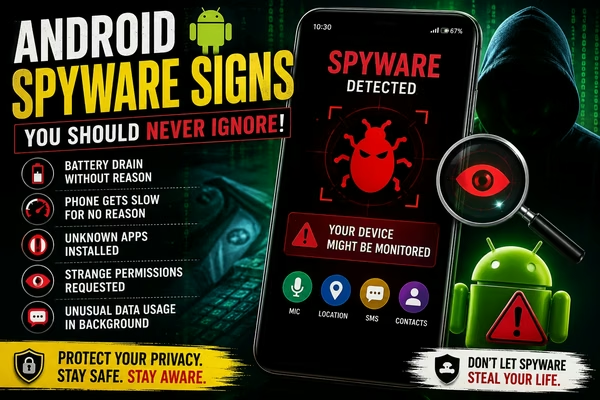
Android Spyware Detection Guide: Find and Remove Hidden Spyware
Learn how to detect hidden spyware on your Android phone, understand stalkerware, remove malicious apps, and protect your device from surveillance tools.
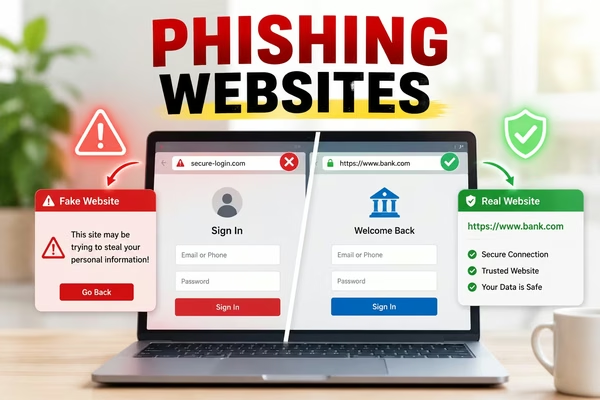
How Phishing Websites Steal Your Data and How to Stay Safe
Understand how fake phishing websites are created, how they harvest your passwords and credit card details, and the best ways to identify and avoid them.
🛡️ Comprehensive Digital Security & Cyber Threat Mitigation Directory
Operating under the Tyagi MultiTech network, this security portal serves as an authentic guide to keep users, developers, and students safe from modern cyber threats. Our mission is to transform complex internet attacks into simple and practical educational resources so that every user can safeguard their digital identity.
🛡️ 1. Advanced Phishing Protection and Social Engineering Defense
Modern cyber attacks are no longer limited to simple deceptive emails. Today, sophisticated social engineering architectures utilize strategies like targeted phishing, spear-phishing, and SIM swap fraud, whose primary objective is to disrupt server telemetry and steal sensitive credentials. Within the Tyagi MultiTech network, it is strongly recommended to strictly verify the official URL structure (URL Canonical Setup) and domain security parameters before entering any personal data.
🔑 2. Robust Two-Factor Authentication (2FA) and Identity Preservation
In the growing era of database leaks and credential stuffing attacks, relying solely on a strong password can prove to be highly insecure. To make your security framework impenetrable, mandatory activation of Multi-Factor Authentication (MFA) or Two-Factor Authentication (2FA) is required. Instead of traditional network SMS-based OTPs, one should use authentication applications or hardware security tokens.
💻 3. Client-Side Device Hardening and Performance Optimization
Minimizing your personal data footprint and continuously revoking unnecessary application permissions is extremely vital. The core operating system security of a device can be strengthened by blocking browser extensions and unwanted background tracking scripts. Additionally, removing excessive inline styling from the code structure and utilizing clean Semantic HTML maximizes site loading speeds.
🌐 4. Network Traffic Encryption and Secure Wi-Fi Management
Using insecure open Wi-Fi networks in public places acts as a direct invitation to Man-in-the-Middle (MITM) attacks. Unencrypted data packets can be easily intercepted using sniffing tools, increasing the risk of leaking financial transactions and personal tokens. Always use an end-to-end encrypted tunnel (such as VPN protocols) and Secure Sockets Layer (HTTPS) when connecting to remote servers.
📊 5. Database Security, SQL Injection, and Leak Prevention
The security of websites and web applications directly depends on their backend database management. Due to weak input sanitization, attackers use SQL Injection (SQLi) to access sensitive tables, which subsequently causes massive data leaks. To eliminate these severe vulnerabilities, always implement parameterized queries and Object-Relational Mapping (ORM) patterns.
⚙️ 6. Malware Payload Analysis and Endpoint Protection
Unverified scripts downloaded from the internet, cracked software, and hidden payloads are the primary sources of backdoor malware or ransomware. This malicious code injects itself into background processes, affecting CPU clock cycles and stealing user data. For effective endpoint protection, enforce a strict sandboxing environment at the system level.
☁️ 7. Cloud Infrastructure Hardening and Identity Access Management
As modern applications migrate to serverless microservices and distributed storage buckets (AWS S3, GCP Cloud Storage), securing cloud environments is essential. Enforce Least Privilege Access Control via strict Identity & Access Management (IAM) configurations. Frequently rotate active API keys, secure environmental configurations (.env variables), and restrict public read-write bucket permissions.
🔑 8. Zero-Trust API Endpoint Security and Token Sanitization
Weak client-to-server API structures allow malicious threat vectors to perform unauthorized CRUD operations. Implement Zero-Trust verification protocols by sanitizing request bodies and headers. Enforce secure JSON Web Tokens (JWT) storage in HTTP-Only cookies, configure strict Cross-Origin Resource Sharing (CORS) rules, and deploy API rate limiters to deflect brute-force DoS attempts.
📋 9. System-Level Backup Automation and Incident Recovery Plans
In the event of a catastrophic system intrusion or host compromise, rapid incident recovery reduces service downtime. Establish automated cron backups for database files, isolated off-site storage instances, and automated log analysis. Continuously audit host server access logs, configure firewalls (UFW), and monitor open active network ports.
Unwavering Trust in Digital Security Principles
Our objective is to spread cyber security awareness and deliver defensive knowledge rather than encouraging or teaching any form of illegal hacking techniques. All suggestions and technical modules included in this directory are designed to promote practical learning, data privacy, and responsible online behavior.
Strict Review and Editorial Policy
Every technical block published under this security directory is thoroughly researched and rigorously verified for absolute factual accuracy. This content is updated at regular intervals based on evolving global security standards, new data breach patterns, and emerging network threats.
Comments & Reviews
Tap stars to rate this page:
